Machine Images
Machine images are a fundamental part of Compute services. A machine image is a single file which contains a virtual disk on which a bootable operating system is installed. It allows a user to create a VM instance with any OS.
Image Requirements
Machine images can be created from the following source formats:
VMware OVA image.
KVM compatible image in RAW or QCOW2 formats.
Note
Openstack KVM images can be used with the KVM compatible image option.
Supported images must meet the following requirements:
The image must be a single bootable system disk.
The image must be configured to receive a network address via DHCP.
User access to the VM instance is required and depends on the image type:
Windows Image - use VNC or enable Remote Access Service.
Linux Image - use SSH server service.
Image Creation
See the video on the basics of zCompute Machine Images and ISOs:
Images can be created from different UI views.
Create Images from Machine Image View
To create image from Machine Image view:
Navigate to the Main menu > Machine Images view and select Images.
In the displayed image list view, click Create in the top toolbar.
The Create Image window opens.
In the Create Image window, configure the following:
Name - name that will identify the image.
Description - description that will help identify the image purpose.
Firmware Type - The low-level software interface used to initialize hardware and boot the operating system.
Select one of:
UEFI (Unified Extensible Firmware Interface):
The modern, firmware standard that replaces legacy BIOS, offering enhanced security through Secure Boot, and support for massive storage drives using the GUID Partition Table (GPT).
Secure Boot + TPM checkbox displays when UEFI is selected.
Mark the checkbox to apply Secure Boot and TPM.
Caution
Leaving the checkbox blank applies UEFI with neither Secure Boot nor TPM.
Note
Secure Boot + TPM is available from zCompute version 25.06.1.
Windows 11 will not install at all without UEFI, Secure Boot, and TPM 2.0. Windows Server 2025 increasingly expects them as well.
BIOS (Basic Input/Output System):
The legacy Basic Input/Output System. The first software that runs after a computer starts, BIOS performs hardware initialization during the booting process and provides runtime services for operating systems, applications and IO devices (keyboard, mouse, display).
BIOS has neither Secure Boot nor TPM.
Operating System - select the required operating system.
Scope - determines which users can access this image:
Project - only users with access to the project.
Account - all account users.
Tags - attach one or more tags to the image.
Click Next to continue to the Setup tab.
In the Setup tab, configure:
Create Image From: - the source to use for creating the new image. When you select one of the source options, the next field is updated as follows:
File - configure:
Volume Type - select the volume type from the dropdown list.
File - drag the image file into the File box, or browse to the file and select it.
URL - configure:
Volume Type - select the volume type from the dropdown list.
Use Legacy IDE - select legacy IDE or native IDE.
Override Size - select whether to keep the image the same size or to override it. To override the size, enter the new size.
Disk Type - select whether to attach the image file as a Disk or CDROM.
Click Add to configure an additional mapping.
Snapshot/Volume - configure:
Snapshot/Volume - source to be used to create image.
Volume Type - select the volume type from the dropdown list.
Use Legacy IDE - select legacy IDE or the native IDE.
Override Size - select whether to keep the image the same size or to override it. To override the size, enter the new size.
Disk Type - select whether to attach the image file as a Disk or CDROM.
Click Add to configure an additional mapping.
Click the Finish button. The image begins to be created. When the uploading progress is completed, the Action Succeeded message is displayed.
Create Images from Storage View
New image creation from an existing volume can be done from the storage view as well. Create an image from a volume, either directly from the volume or by using a snapshot of the volume. If the volume is currently not attached to a running VM instance, create an image as described below. If the volume is attached to a running VM instance which can not be stopped, first detach the volume and create a snapshot, and then create an image from the snapshot.
To create an image from a volume in storage view
Navigate to the Storage > Block Storage view.
In the displayed list, select the volume to be used to create the image.
In the top toolbar, select Create Image.
The Create Image From Volume window opens.
In the displayed Create Image From Volume window, configure the following:
Name - name that will identify the image.
Description - description that will help identify the image purpose.
Tags - attach one or more tags to the image.
Operating System - select the required operating system.
Click OK. The new image is displayed in the Machine Images > Images list.
Note
If you select a non-bootable volume as the source of an image, the OS will not boot.
The Create Image From Volume dialog does not include a Firmware Type field. The new image is created with BIOS firmware regardless of the source volume’s actual firmware.
If the source volume uses UEFI, or UEFI with Secure Boot + TPM, set the correct Firmware Type afterwards. See Modifying an Image.
Create Images from Snapshot View
The system permits creation of images from a volume snapshot. Using a volume snapshot as the image source allows the user to create the image without stopping the VM instance or detaching the volume.
To create an image from a snapshot:
Navigate to the Storage > Snapshots view.
In the displayed list, select the snapshot to be used for creating the image and click Create Image from the top toolbar.
The Create Image window opens.
In the displayed Create Image window, enter the Name of the new image.
Firmware Type - The low-level software interface used to initialize hardware and boot the operating system.
Select one of:
UEFI (Unified Extensible Firmware Interface):
The modern, firmware standard that replaces legacy BIOS, offering enhanced security through Secure Boot, and support for massive storage drives using the GUID Partition Table (GPT).
BIOS (Basic Input/Output System):
The legacy Basic Input/Output System. The first software that runs after a computer starts, BIOS performs hardware initialization during the booting process and provides runtime services for operating systems, applications and IO devices (keyboard, mouse, display).
BIOS has neither Secure Boot nor TPM.
Warning
This field defaults to BIOS.
A volume snapshot carries no record of the source VM instance’s original firmware. If you accept the default and the source was UEFI, every VM instance later launched from this image starts as BIOS and will not boot. Set Firmware Type, and Secure Boot + TPM if applicable, to match the source before clicking OK.
Click OK. The new image is displayed in the Machine Images > Images list.
Creating ISO Images
ISO images can only be created from the Machine Images UI view.
Navigate to the Main menu > Machine Images view and select Images.
In the displayed image list view, click Create ISO from the top toolbar.
In the displayed Create ISO Image window, configure the following:
Name - name that will identify the image.
Note
When creating an ISO image in Zadara Cloud Services, the name of the image must end with the ‘.iso’ extension.
Description - description that will help identify the image purpose.
Firmware Type - The low-level software interface used to initialize hardware and boot the operating system.
Select one of:
UEFI (Unified Extensible Firmware Interface):
The modern, firmware standard that replaces legacy BIOS, offering enhanced security through Secure Boot, and support for massive storage drives using the GUID Partition Table (GPT).
Secure Boot + TPM checkbox displays when UEFI is selected.
Mark the checkbox to apply Secure Boot and TPM.
Caution
Leaving the checkbox blank applies UEFI with neither Secure Boot nor TPM.
Note
Secure Boot + TPM is available from zCompute version 25.06.1.
Windows 11 will not install at all without UEFI, Secure Boot, and TPM 2.0. Windows Server 2025 increasingly expects them as well.
BIOS (Basic Input/Output System):
The legacy Basic Input/Output System. The first software that runs after a computer starts, BIOS performs hardware initialization during the booting process and provides runtime services for operating systems, applications and IO devices (keyboard, mouse, display).
BIOS has neither Secure Boot nor TPM.
Operating System - select the required operating system.
Volume Type - select the volume type from the dropdown list.
Scope - determines which users can access this image:
Project - only users with access to the project.
Account - all account users.
Tags - attach one or more tags to the image.
Click Next.
The Setup > OS Installation Disk window is displayed.
Depending on the selected source option, configure the next field as follows:
File - drag the image file into the File box, or browse to the file and select it.
Snapshot/Volume - configure the source snapshot/volume to be used to create image.
URL - enter the URL of the image file and check Skip SSL verification if needed.
For ISO image creation, select Add Drivers to include drivers for use during and after the operating system installation. The additional drivers disk can be created from an existing file or snapshot/volume.
Click Finish. The ISO Image is displayed in the Images list.
Creating an image from a VM Instance
To create an image directly from a VM instance:
Navigate to the Compute > Instances view.
From the displayed list, select the VM instance to capture, and click More.
In the More menu, select Create image.
In the Create Image From VM window, configure:
Name - a name that will identify the new image.
Description - a description that will help identify the image’s purpose.
Tags - attach one or more tags to the image.
Reboot - selected by default. It is recommended to leave it selected. Clearing this setting displays a warning that rebooting is recommended to avoid image corruption.
Click OK. The new image is displayed in the Machine Images > Images list.
Note
There is no Firmware Type field on this dialog. The new image automatically inherits the source VM instance’s firmware setting, including Secure Boot + TPM if the instance has it enabled.
See Viewing an Image’s Firmware and Secure Boot Status to confirm the captured image’s setting, and Secure Boot and vTPM for background on Secure Boot and vTPM.
Windows Server VM Instance Creation
Note
The recommended best practice is to use a Zadara or partner-provided Windows Server image, which is already preinstalled with virtio drivers and Cloudbase-init.
This procedure creates a BIOS-firmware instance and manually injects VirtIO drivers. It does not use the Secure Boot + TPM available from zCompute version 25.06.1.
For Windows 11 it is required to use a UEFI-based Windows image and select UEFI with Secure Boot + TPM when creating the ISO image and the VM instance. See Windows Instances and Secure Boot + vTPM, Image Creation and Modify a VM Instance.
The following section describes how to create a new Windows Server 2019 VM Instance from an ISO in the zCompute Compute Cloud.
The latest version of virtio drivers has an installer to simplify the installation.
To create a Windows Server Instance:
Create the Image.
Navigate to Machine Images > Images.
From top toolbar, click Create ISO.
The Create ISO Image dialog opens.
In the Create ISO Image dialog’s Details tab, enter the following:
Name
Firmware Type - select BIOS.
Operating System - select the Windows OS version.
Volume Type - select the volume type from the dropdown list.
Scope (cloud admin view only) - select Account.
Click Next to continue to the Setup tab.
In the Setup tab, click Add Drivers.
Select URL (or File if images are available locally), and enter the following URLs:
OS Installation Disk - Windows ISO.
Additional Drivers Disk - <https://zadarastorage-software.s3.us-east-1.amazonaws.com/Windows-ISOs/virtio-win-1.9.15.iso>
Click Finish.
After the upload has completed, navigate to Compute > Instances.
From the top toolbar, click Create.
The Create VM dialog opens.
In the Create VM dialog Setup tab, enter the following:
Name - a name that will identify the VM instance.
Project - the VM instance must be created within a project.
Create From - select ISO.
Installation ISO - select the ISO image.
Instance Type - select the instance type with the desired instance size.
Operating System - select the image’s operating system.
Click Next through the Storage and Network tabs, and Finish on the Config tab.
After the instance has been spawned and has the status Active, navigate to Compute > Instances.
Select the image and click Connect from top toolbar.
Run Windows Setup to continue with the Windows Server installation.
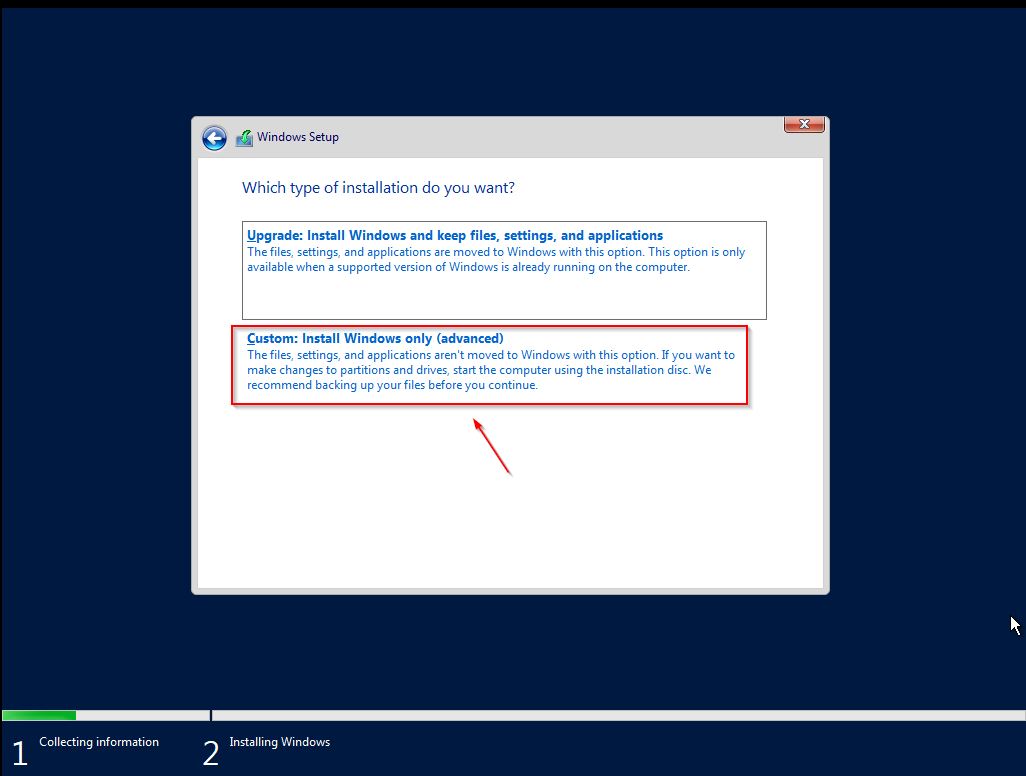
When prompted for Type of Installation, select Custom.
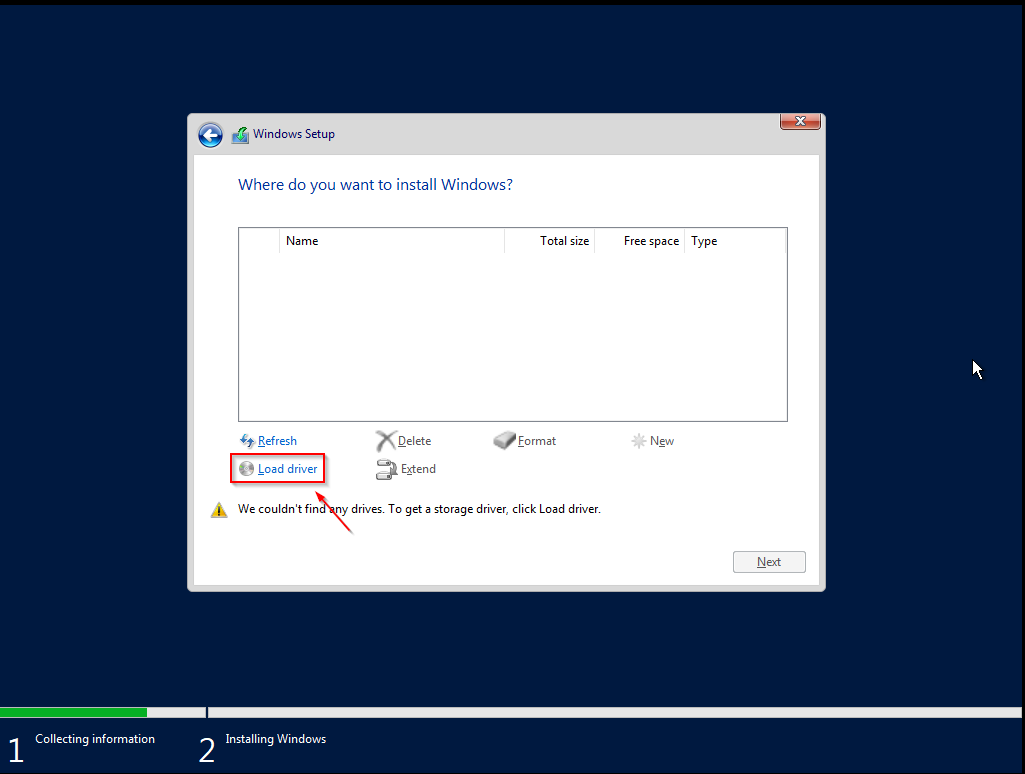
When prompted with Where do you want to install Windows, select Load Driver.
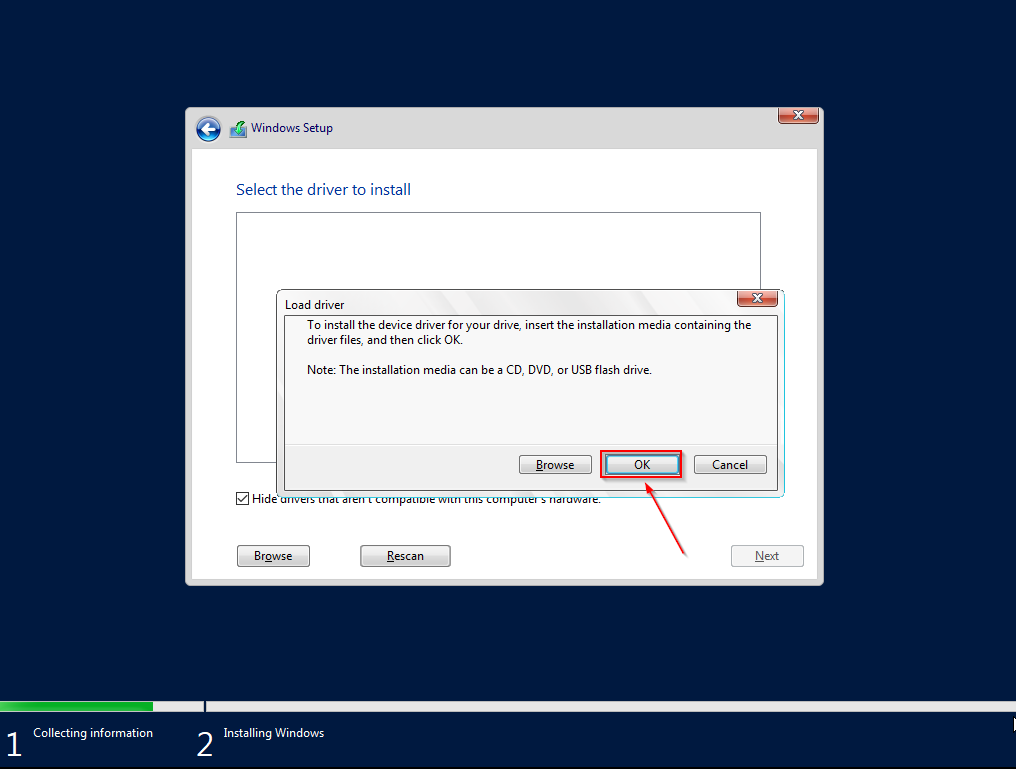
When prompted to Load Driver click OK.
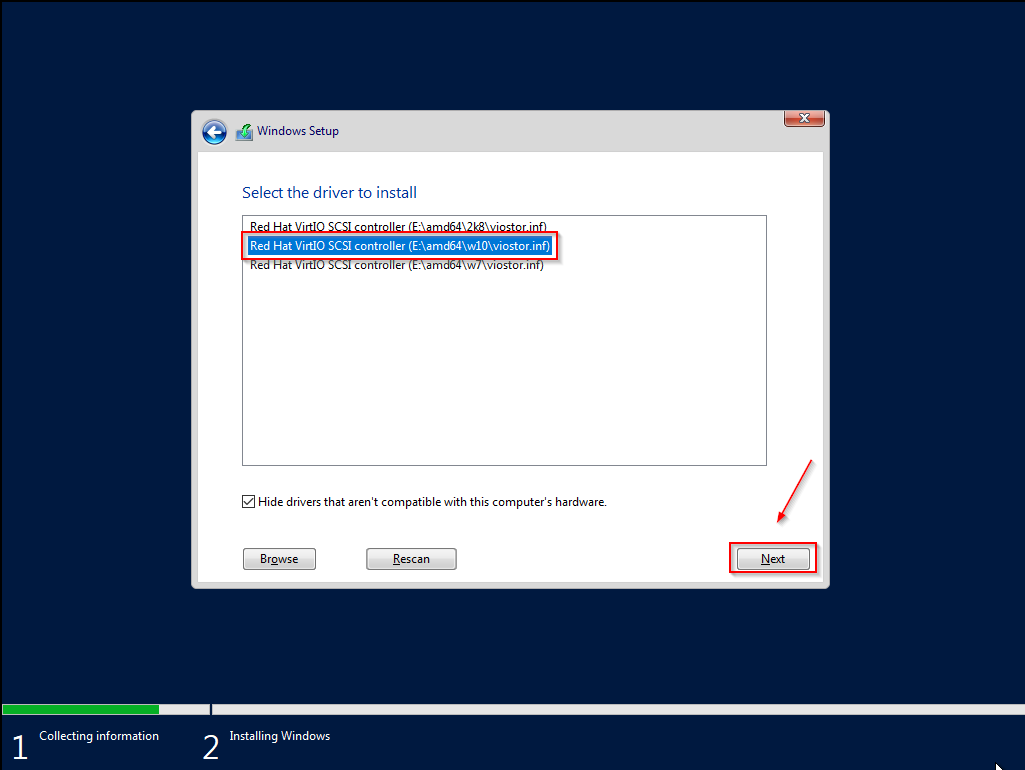
Select the Red Hat VirtIO SCSI controller (E:\amd64\w10\viostor.inf) option and select Next.
Continue as prompted by install wizard for the rest of the installation.
After Windows has been installed, log into Windows as Administrator.
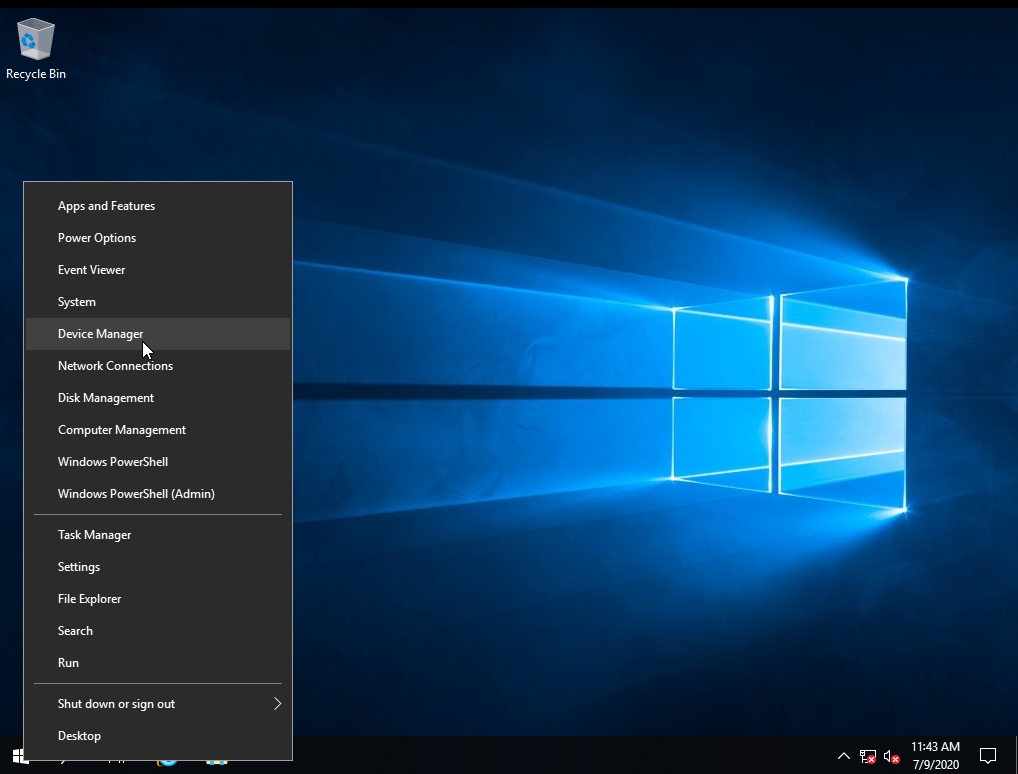
Right-click on the Start Menu and select Device Manager.
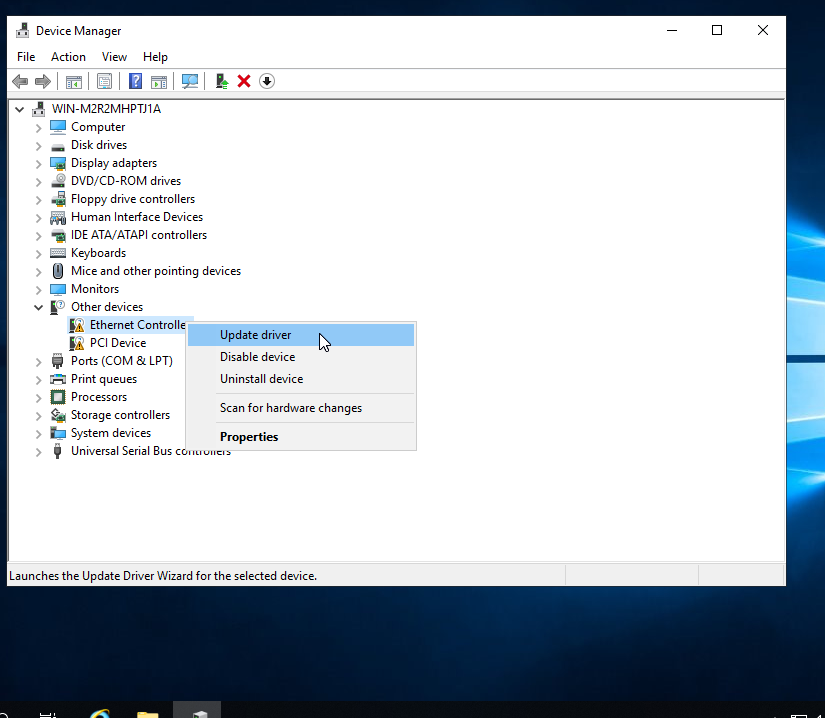
Right-click on Ethernet Controller and select Update driver.
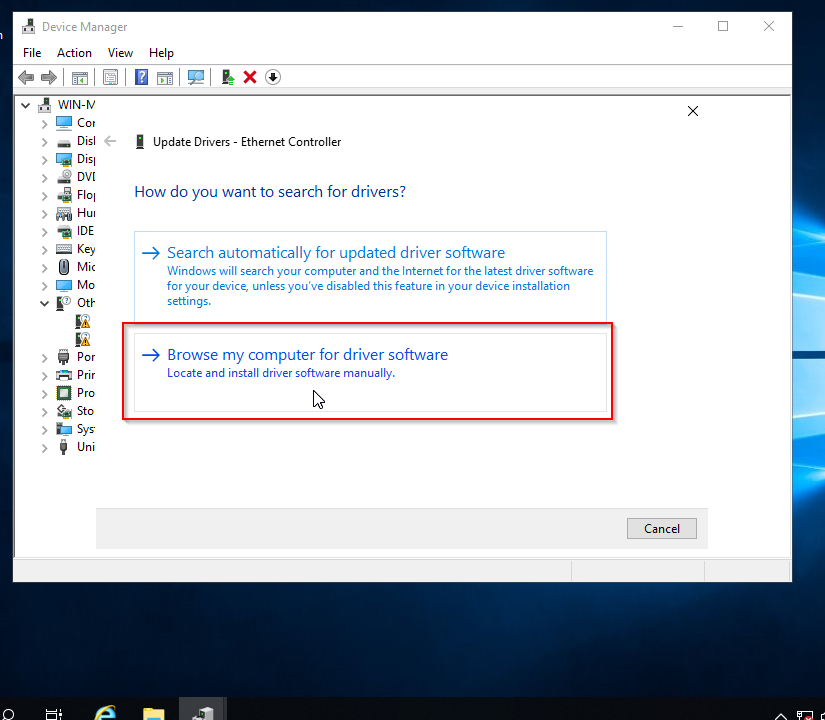
Select Browse my computer for driver software.
Select Browse and select the CD Drive (virtio-win-x.x.x).
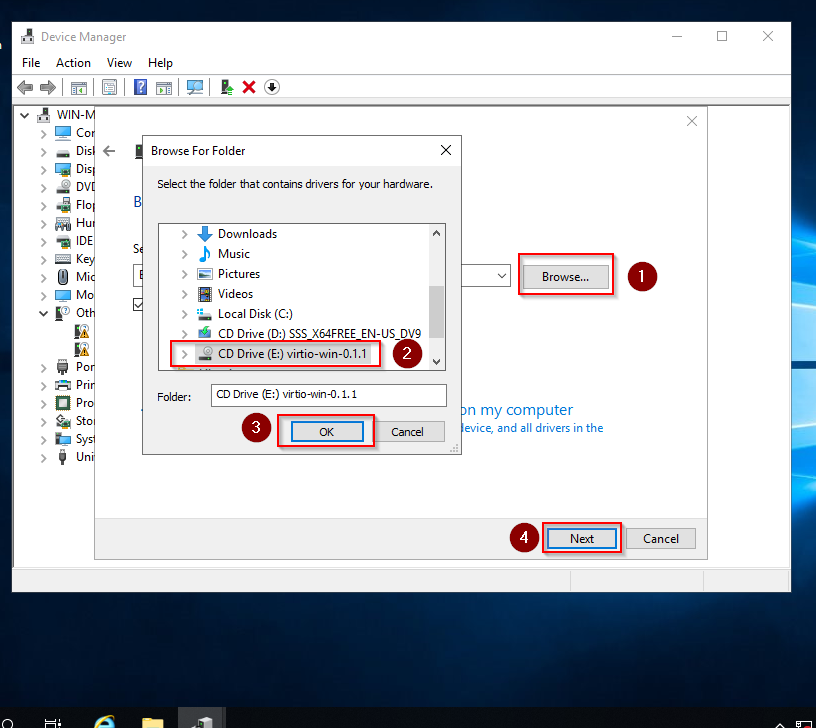
Click OK.
Click Next.
When prompted by Windows Security, select Install.
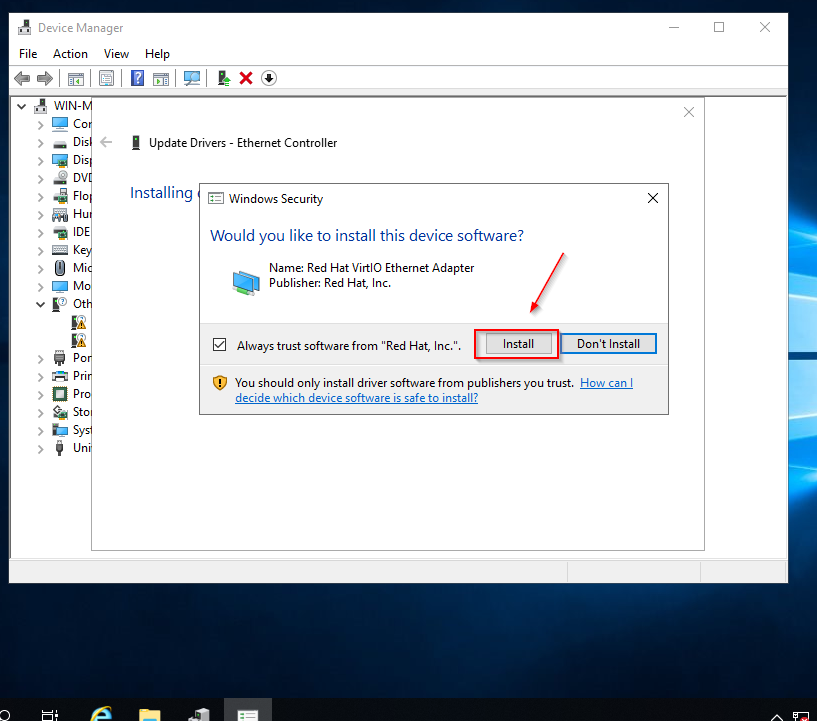
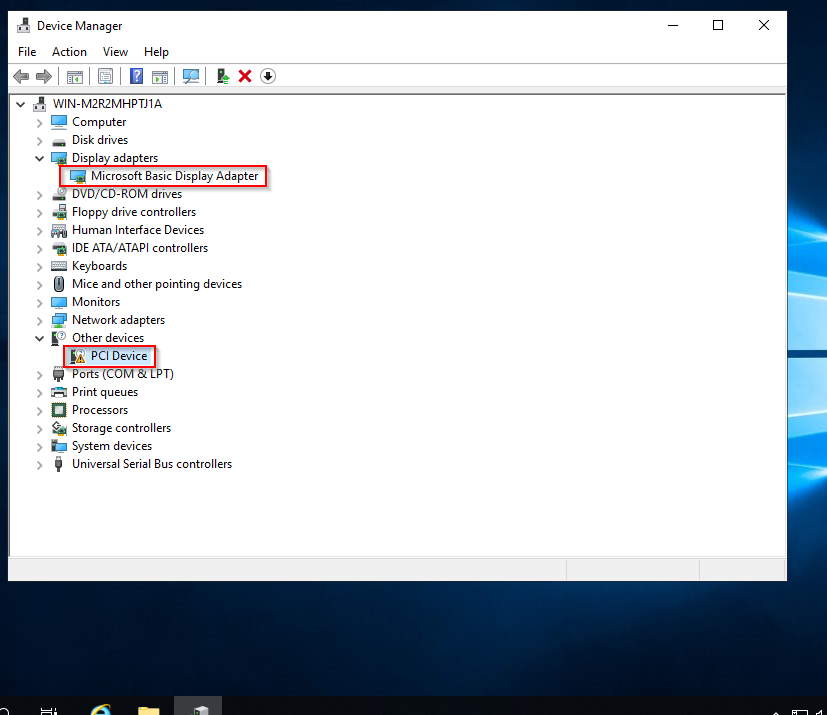
Repeat this process for the Display Adapter and also for Other Device > PCI Device.
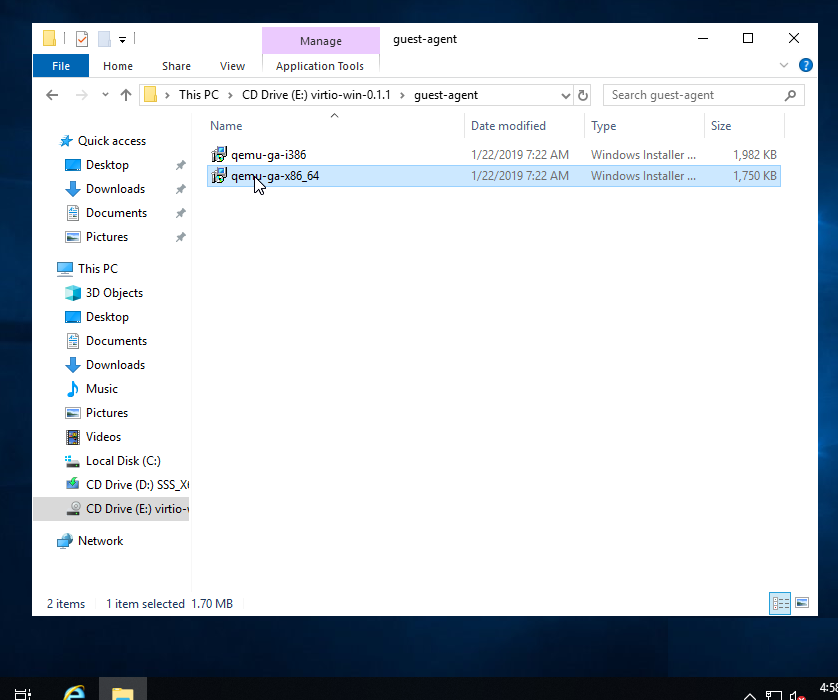
To complete installation, open Windows Explorer and install QEmu agent.
Correcting Windows VM RAM consumption display in zCompute
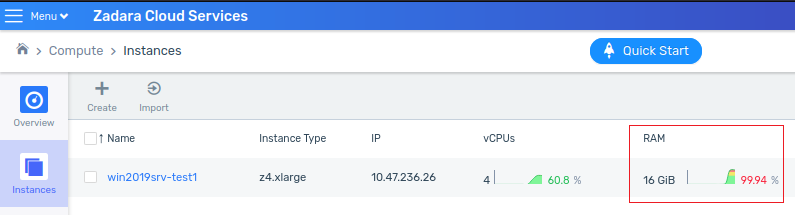
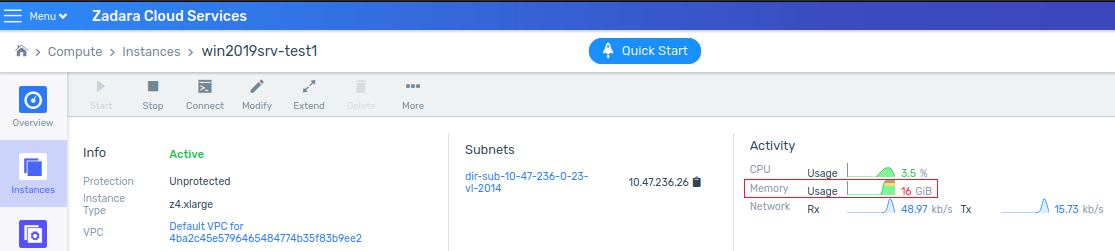
It is common to see that zCompute UI Compute > Instances reports Windows VMs consuming 100% of the RAM allocated to them, although the OS actually uses much less RAM.
For example, an incorrect reflection of a VM’s RAM consumption:
In the Compute > Instances list:
In the Compute > Instances > <VM> detail screen:
The actual RAM consumption according to the VM’s Windows Task Manager screen:
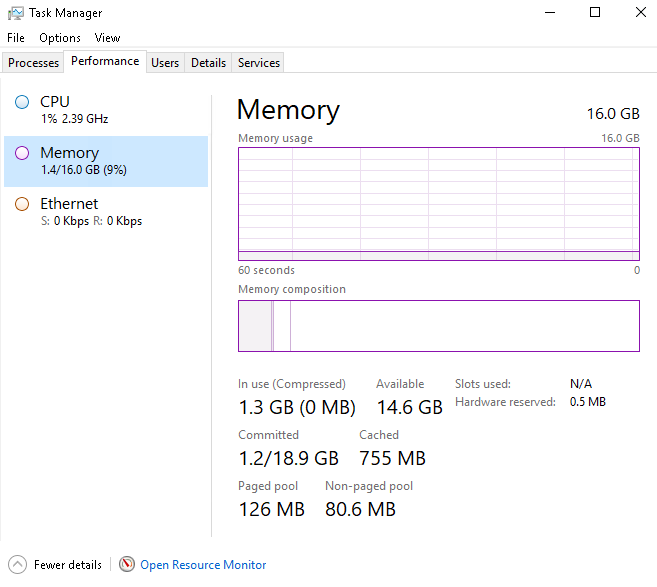
In most cases, the reason for this discrepancy is that the guest VM OS doesn’t have the Windows VirtIO Balloon driver and service properly installed, or that they’re outdated.
To rectify the display, you must download and install the Win VirtIO Guest Tools package, which installs the Balloon driver and service together with any other missing VirtIO drivers on the VM:
Sign in to the Windows VM.
Download the VirtIO Guest Tools MSI installer from the Win-VirtIO archives website:
https://fedorapeople.org/groups/virt/virtio-win/direct-downloads/stable-virtio/virtio-win-gt-x64.msi
Right click the downloaded installer and click Install.
Accept the terms.
In the Custom Setup screen select only the following components to install:
Balloon
Network
Viostor
Disable the installation of all other components.
Warning
Do not install the rest of the MSI installer components.
They are not in use and not tested, and could only expose the guest VM to potential threats, by adding to the VM’s attack surface.
Allow the VM to reboot when prompted by the Installer.
In the zCompute UI, stop the VM:
Go to Compute > Instances > <VM instance>.
Click Stop and wait for the VM instance to reach the Shutoff status.
In the zCompute UI, restart the VM:
Go to Compute > Instances > <VM instance>.
Click Start and wait for the VM instance to reach the Active status.
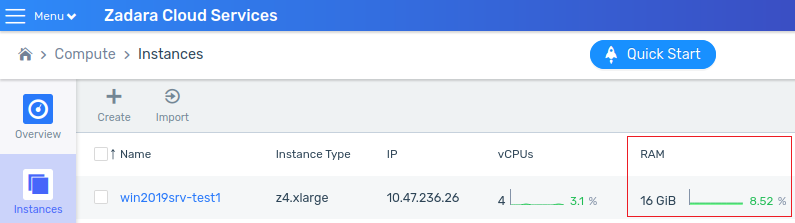
The zCompute UI should now report the VM’s correct RAM consumption for example:
In the Compute > Instances list:
In the Compute > Instances > <VM> detail screen:
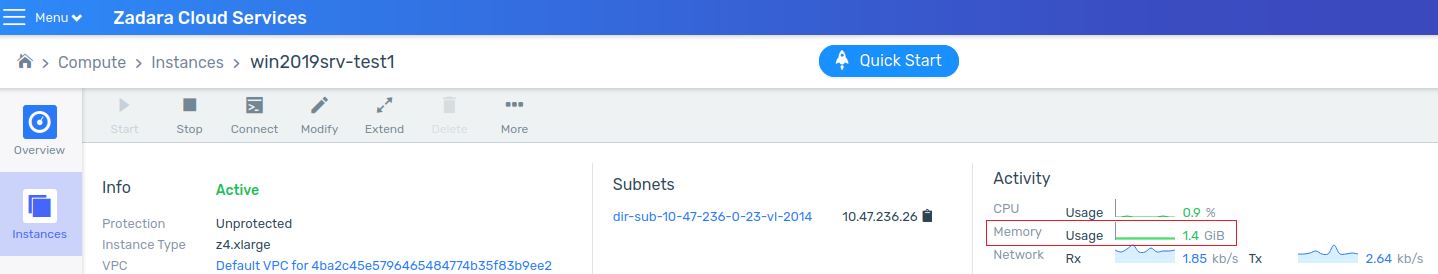
The zCompute UI’s VM RAM usage values in this example now correctly reflect the actual RAM consumption according to the VM’s Windows Task Manager screen:
Note
Installation of the Win VirtIO Balloon driver and service has no effect on memory reserved by the system for VMs.
Memory reserved by the system is the size of the VM, without over-commitment or over-allocation.
Viewing an Image’s Firmware and Secure Boot Status
To check an image’s current firmware and Secure Boot setting:
Navigate to the Main menu > Machine Images view and select Images.
In the column picker, enable the Firmware Type and Secure Boot columns. They are hidden by default.
Warning
The Firmware Type column alone does not distinguish a Secure Boot image from a plain UEFI image. Both display as UEFI.
Add the separate Secure Boot column, or open the image.
To check a single image, open it. Its Summary panel lists Firmware Type and Secure Boot + TPM as separate rows.
Modifying an Image
To modify an existing image’s firmware or Secure Boot setting:
Navigate to the Main menu > Machine Images view and select Images.
Select the image, and click Modify.
In the Modify Image dialog, update:
Firmware Type - The low-level software interface used to initialize hardware and boot the operating system.
Note
Changing the image’s Firmware Type doesn’t change the image’s content (boot loader, boot disk structure, etc.). The image’s firmware defines how the emulated VM hardware will try to boot the OS. If these don’t match, the boot will fail.
Select one of:
UEFI (Unified Extensible Firmware Interface):
The modern, firmware standard that replaces legacy BIOS, offering enhanced security through Secure Boot, and support for massive storage drives using the GUID Partition Table (GPT).
Secure Boot checkbox displays when UEFI is selected.
Mark the checkbox to apply Secure Boot and TPM.
Caution
Leaving the checkbox blank applies UEFI with neither Secure Boot nor TPM.
Note
Secure Boot + TPM is available from zCompute version 25.06.1.
BIOS (Basic Input/Output System):
The legacy Basic Input/Output System. The first software that runs after a computer starts, BIOS performs hardware initialization during the booting process and provides runtime services for operating systems, applications and IO devices (keyboard, mouse, display).
BIOS has neither Secure Boot nor TPM.
Note
These fields are editable only by a system administrator. Other users can view, but not change, an existing image’s firmware and Secure Boot setting.
Click OK.
Cloning an Image
To clone an image, including its firmware and Secure Boot setting:
Navigate to the Main menu > Machine Images view and select Images.
Select the image, and click Clone.
In the Clone Image dialog’s Details step, the cloned image’s Firmware Type and Secure Boot + TPM can be reviewed and changed before the clone is created:
Firmware Type - The low-level software interface used to initialize hardware and boot the operating system.
Select one of:
UEFI (Unified Extensible Firmware Interface):
The modern, firmware standard that replaces legacy BIOS, offering enhanced security through Secure Boot, and support for massive storage drives using the GUID Partition Table (GPT).
Secure Boot checkbox displays when UEFI is selected.
Mark the checkbox to apply Secure Boot and TPM.
Caution
Leaving the checkbox blank applies UEFI with neither Secure Boot nor TPM.
Note
Secure Boot + TPM is available from zCompute version 25.06.1.
Windows 11 will not install at all without UEFI, Secure Boot, and TPM 2.0. Windows Server 2025 increasingly expects them as well.
BIOS (Basic Input/Output System):
The legacy Basic Input/Output System. The first software that runs after a computer starts, BIOS performs hardware initialization during the booting process and provides runtime services for operating systems, applications and IO devices (keyboard, mouse, display).
BIOS has neither Secure Boot nor TPM.
Complete the remaining wizard steps and click Finish.
Deleting Images
Navigate to the Main menu > Machine Images view and select Images.
From the displayed list, select an image and click Delete from the top toolbar.
The Delete Image confirmation window opens.
In the Delete Image window, click Delete to confirm deletion of the image.
The Image is deleted, and Action Succeeded message is displayed.
Machine Images Marketplace
The following tested images can be downloaded from the Machine Images > Marketplace view.
Zadara
Zadara EKS-D ver. 1.28, ver. 1.29, ver. 1.30
Zadara zCompute Toolbox Ubuntu ver. 3.0.4
Operating Systems: Cloud Images
Alma Linux ver. 9, ver. 10
CirrOS ver. 0.5.1
Debian ver. 11, ver. 12, ver. 13
Fedora ver. 44
Rocky Linux ver. 9, ver. 10
Ubuntu Jammy ver. 22.04-LTS
Ubuntu Noble Numbat ver. 24.04-LTS
Ubuntu Resolute Raccoon ver. 26.04-LTS
Virtual Appliances: Cloud Images
Backup2Cloud Linux Appliance 14.2.0 Ubuntu 24.04
Backup2Cloud Linux Appliance 14.2.0 Windows Server 2022
Loadbalancer Enterprise ADC ver. 8.9.0
pfSense-CE ver. 2.7.2
To download an image from the Zadara Marketplace:
Navigate to the Machine Images > Marketplace view.
Select the image to download.
In the image window that opens, enter the following:
Volume Type - select the volume type from the dropdown list.
Scope - determines which users can access this image:
Project - only users with access to the project.
Account - all account users.
Firmware Type: The software that provides low-level control of computing device hardware.
Note
From zCompute 25.06, it is possible to override the image’s default Firmware Type.
Select one of:
BIOS: The legacy Basic Input/Output System. The first software that runs after a computer starts, BIOS performs hardware initialization during the booting process and provides runtime services for operating systems, applications and IO devices (keyboard, mouse, display).
UEFI: The newer Unified Extensible Firmware Interface, that replaces legacy BIOS.
Click Download. A new image is registered in the system and will appear in the image list.
AWS Image Import API
The following table describes the supported AWS APIs for Image operations:
AWS API Name |
Ignored Params |
Optional Params |
Required Params |
Unsupported Params |
|---|---|---|---|---|
ImportTaskId MaxResults NextToken |
||||
[] |
Architecture ClientData ClientToken Description DiskContainer Hypervisor LicenseType Platform RoleName |
[] |
[] |